Australia has strong cyber security frameworks, mature regulatory settings and clear expectations for the protection of critical systems and citizen data. But as government agencies adopt cloud, analytics and AI at pace, cyber security leaders are being forced to ask a more difficult question: is compliance enough?
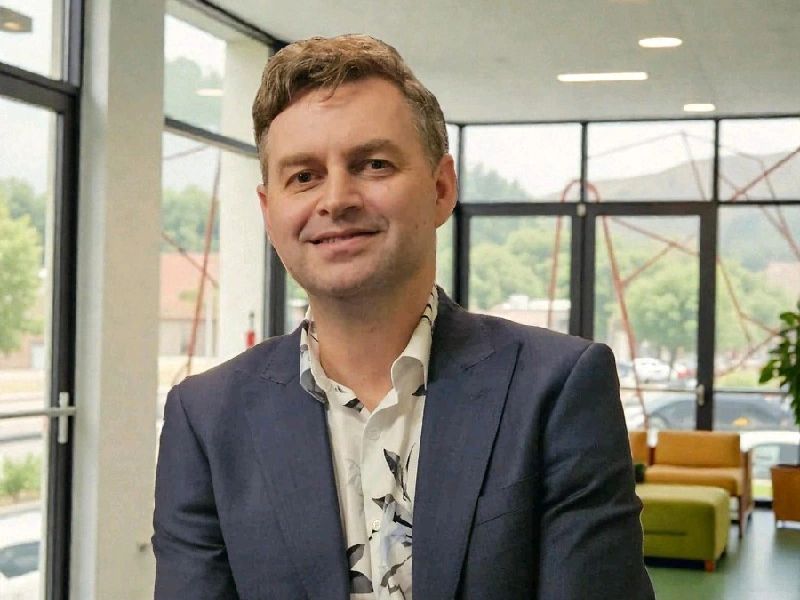
In the latest episode of Delivery: A GovTech Podcast, InnovationAus.com publisher Corrie McLeod speaks with Matthew White, Thales’ vice-president of cyber security specialists for APJ, about the gap between compliance-driven security and genuine operational resilience.
Mr White leads a regional team of cyber security and platform specialists working with government and enterprise customers across APJ. Much of that work, he says, starts with compliance – from global frameworks such as PCI DSS 4.0 and GDPR, through to Australia’s regulatory and policy settings, including the Australian Prudential Regulation Authority (APRA)’s CPS 230 and CPS 234, the Security of Critical Infrastructure (SOCI) Act, the Essential Eight and controls spanning application and data security. But compliance should be treated as the baseline, not the destination.
“Australia has a very strong baseline. We talk about things such as Essential Eight and the Security of Critical Infrastructure (SOCI) Act,” Mr White says.
“But I think customers or government bodies can sometimes treat that baseline as the destination. I think we’ve got to take a more holistic approach around maturity levels and around some of these compliance mandates.”
Mr White says many agencies that reach maturity level two under the Essential Eight can be tempted to “declare victory”, when the real challenge is to keep moving towards higher maturity and a sharper focus on protecting the data itself.
The pressure to move further is also backed by law. Australia’s Cyber Security Act 2024, alongside amendments to the SOCI Act, has expanded the compliance landscape for organisations managing sensitive systems and data. At the same time, regulatory obligations such as APRA’s CPS 230 on operational risk management and CPS 234 on information security have sharpened expectations for resilience, accountability and third-party risk.
Compliance has evolved to an expanding set of obligations that must be actively tracked — from global privacy and payment-security requirements through to local cyber, infrastructure and prudential standards.
He points to the private sector’s experience with PCI DSS, the global payment card security standard, as an example of a compliance regime that is “laser-focused” on protecting a specific class of sensitive data.
The question for government, he says, is whether similarly focused thinking is being applied to the many categories of citizen data held across federal, state and territory systems.
“Government holds the keys to our identities, whether that’s our driver licence, passport, birth certificate or something else,” Mr White says.
“We’re handing over that identity… to other organisations in order to do business, whether it’s a credit check or something else. But we’re not looking at how we’re securing that data for the long term as well.”
For government, the challenge is more complex than in many enterprise environments. Different jurisdictions hold different types of data, and agencies operate under different legislative, operational and service-delivery obligations. That makes visibility critical.
Mr White says the most mature organisations tend to have a deeper understanding of what data they hold, where it sits, who can access it and how it is being used. In highly sensitive national security environments, this is already well understood, with classified data protected through strict controls and locked-down architectures.
But in other environments, the picture can be less clear.
“With other organisations, they don’t really have visibility around the data they hold,” he says, “which makes it a lot harder to secure.”
That challenge has become more urgent as agencies seek to extract more value from data through analytics, automation and AI.
Ten or 15 years ago, Mr White says, customer data may have sat in a single database, tightly controlled and largely static. Today, data is moving across systems, cloud services, analytics platforms and AI models.
“As customers and as custodians of that data, we don’t always have visibility of where that data is going and who’s accessing it. I think that’s the biggest problem.”
AI has intensified this tension. Public sector organisations are under pressure to use AI to improve productivity and service delivery, but the data risks can be difficult to assess when technology teams move faster than governance, risk and compliance teams can respond.
“AI is still dealing with data. It’s just a different way of dealing with data,” Mr White says.
“The challenge is that it’s moving quicker than we can keep up with governance and risk.” One risk Mr White flags is the proliferation of teams independently deploying AI models (shadow AI), without centralised oversight. “A lot of the answer comes back to data monitoring. The data still lives in our data stores, whether they are structured or unstructured. We really need a clear picture of who is accessing that data, when they are accessing it, and why.”
For government agencies, he says, the starting point should be a disciplined assessment of what data an AI model actually needs to perform its function. Not all data adds value. Some data, such as passport numbers or other personal identifiers, can significantly increase risk without improving the model’s usefulness.
“What data does the AI model need to do its job? What benefits am I getting out of the AI model?” he says.
“If I have to send that data to the AI model, can I protect that data before it actually hits the AI model, or protect it before it’s released from the AI model, depending on my access controls as well?”
Mr White says governance and risk teams are often “playing catch up” as AI adoption accelerates. Questions around sovereignty, storage, deletion and model training are becoming more important, particularly where citizen data or personally identifiable information is involved.
“If I’m dealing with citizen data or personally identifiable information, where is that data being stored, and can I ever delete that data if I’ve made a mistake?” he says.
“These are all questions that are really hard to get an answer for today. If I’m dealing with citizen data or personally identifiable information, where is that data being stored and can I actually ever delete that data if I’ve made a mistake?”
The risk is not theoretical. Mr White points to examples where AI models connected to support systems or internal knowledge bases have been vulnerable to prompt injection, allowing users to extract information that should not have been exposed.
In a government context, the consequences could be far more serious.
“If you think of something like a government body that is dealing with citizen data… if that AI model is not set up correctly, secured correctly, or doesn’t have the right baselines and protections, then something potentially similar could happen,” he says.
“That might be me getting your data… with a very exact prompt, or vice versa, or it could be me getting information that I shouldn’t have from those systems.”
At the same time, Mr White says AI will also become part of the solution. Over the next few years, he expects to see more self-healing systems that can detect breaches, isolate attacks and restore automatically without waiting for human diagnosis.
He also sees AI playing a role in helping organisations prepare for post-quantum cryptography, as governments and critical infrastructure providers assess which cryptographic protections may be at risk in future.
The Australian Signals Directorate (ASD)’s Guidelines for Cryptography advise organisations to identify systems and applications using cryptographic algorithms that are not approved for use beyond 2030, and to develop a plan to transition them to post-quantum cryptography.
According to Thales’ 2026 Data Threat Report, 63 per cent of organisations surveyed in Australia cited future quantum compromise as their top quantum-related concern, while 49 per cent are actively prototyping or evaluating post-quantum cryptography solutions.
But the broader lesson is that resilience should not be measured only by how quickly an organisation can recover after a breach.
“Sometimes we measure resilience by how fast we bounce back,” Mr White says. “After something happens, how quickly can we come back?”
“I think we’ve got to measure resilience around how we can secure these breaches. Rather than how fast we can bring the systems back online… how can we actively protect our systems so if there is a breach, nothing is compromised from a data perspective?”
For government, that means moving beyond the checklist. Compliance remains essential, but the next stage of maturity is a more active, data-centric view of security: knowing what is held, why it is held, where it moves, who can access it and how it is protected if systems are compromised.
As agencies adopt AI and cloud services more deeply, Mr White says the stakes will continue to rise.
“Today, with AI, attacks are happening faster than ever. The risks are higher than ever, but we can secure the systems better than we have in the past.”
This episode of Delivery: A GovTech Podcast was produced in partnership with Thales.
Do you know more? Contact James Riley via Email.